Hiding a DLL from the PEB Loader List (And Why Process Explorer Still Sees It)
Pavel Yosifovich unlinks a DLL from the PEB’s loader module list, compares it to EnumProcessModules,
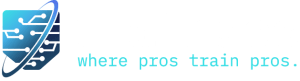

Pavel Yosifovich unlinks a DLL from the PEB’s loader module list, compares it to EnumProcessModules,
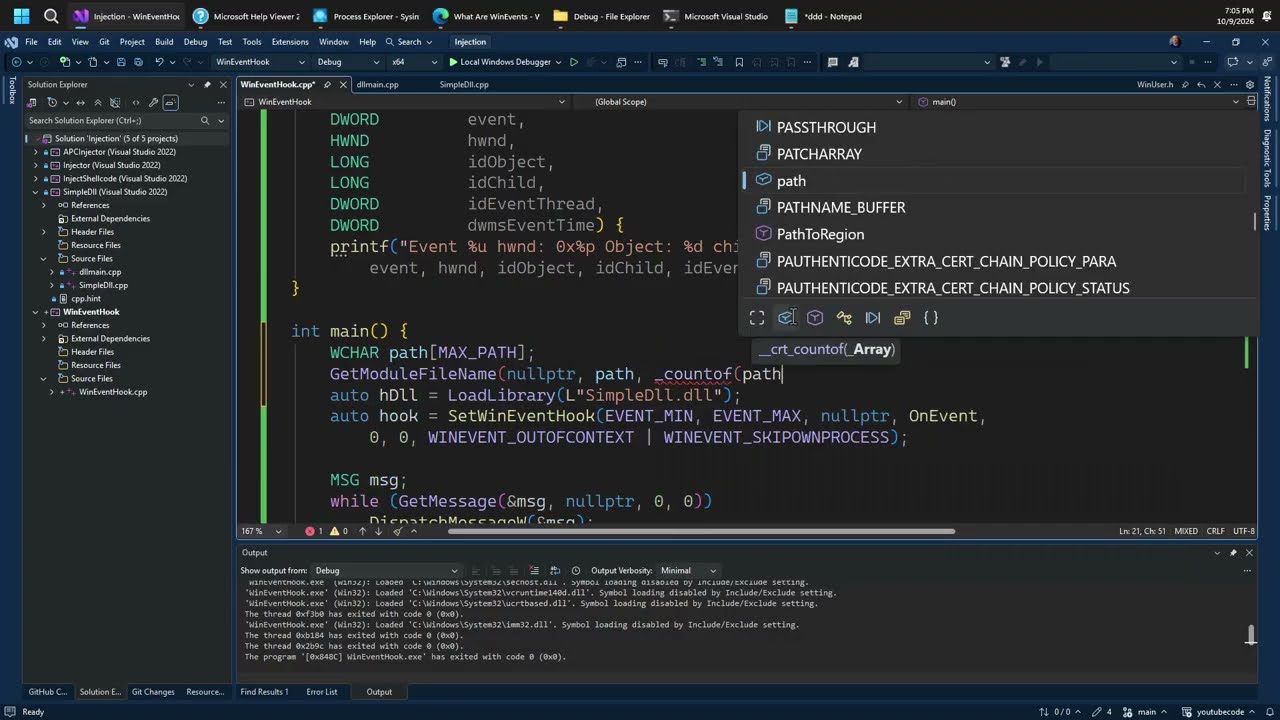
Pavel Yosifovich injects a DLL using SetWinEventHook, the accessibility event hook, covering in-context hooks, the
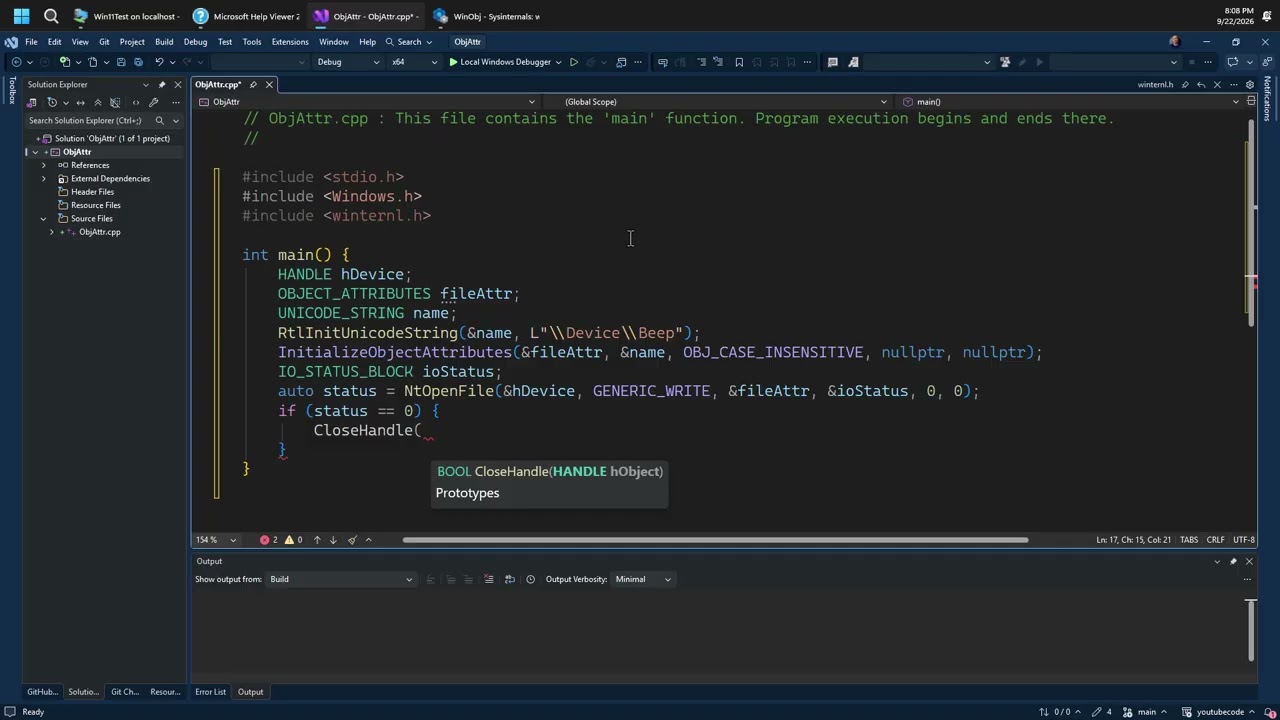
Pavel Yosifovich explains the OBJECT_ATTRIBUTES structure behind every native and kernel create or open call,
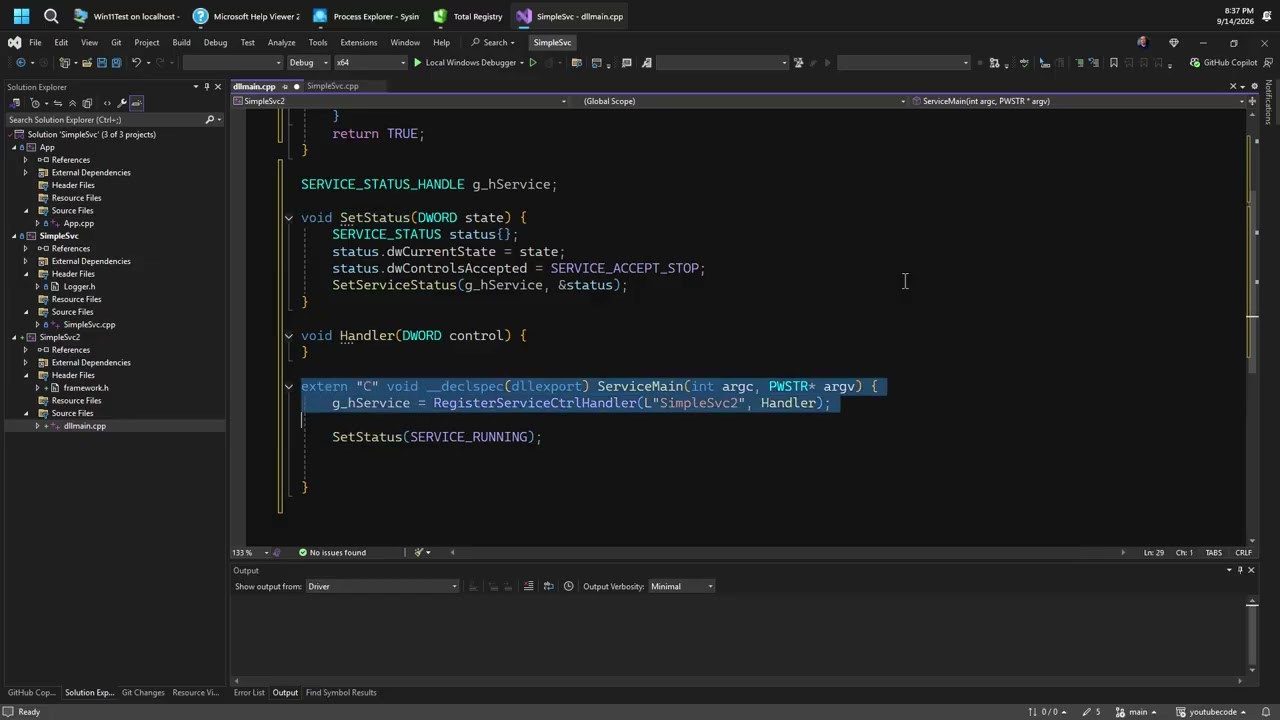
Pavel Yosifovich builds a service DLL that svchost.exe hosts, wiring up ServiceMain, the control handler,
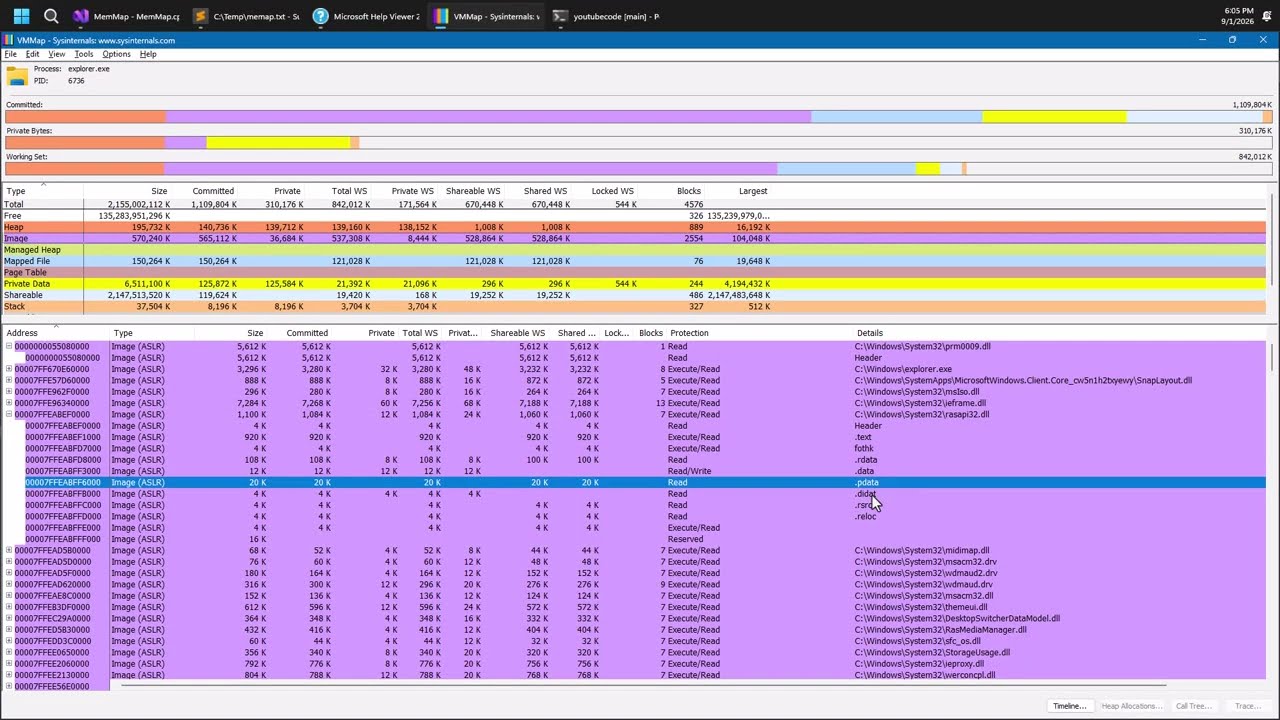
Pavel Yosifovich parses PE headers in a remote process to name the section behind every
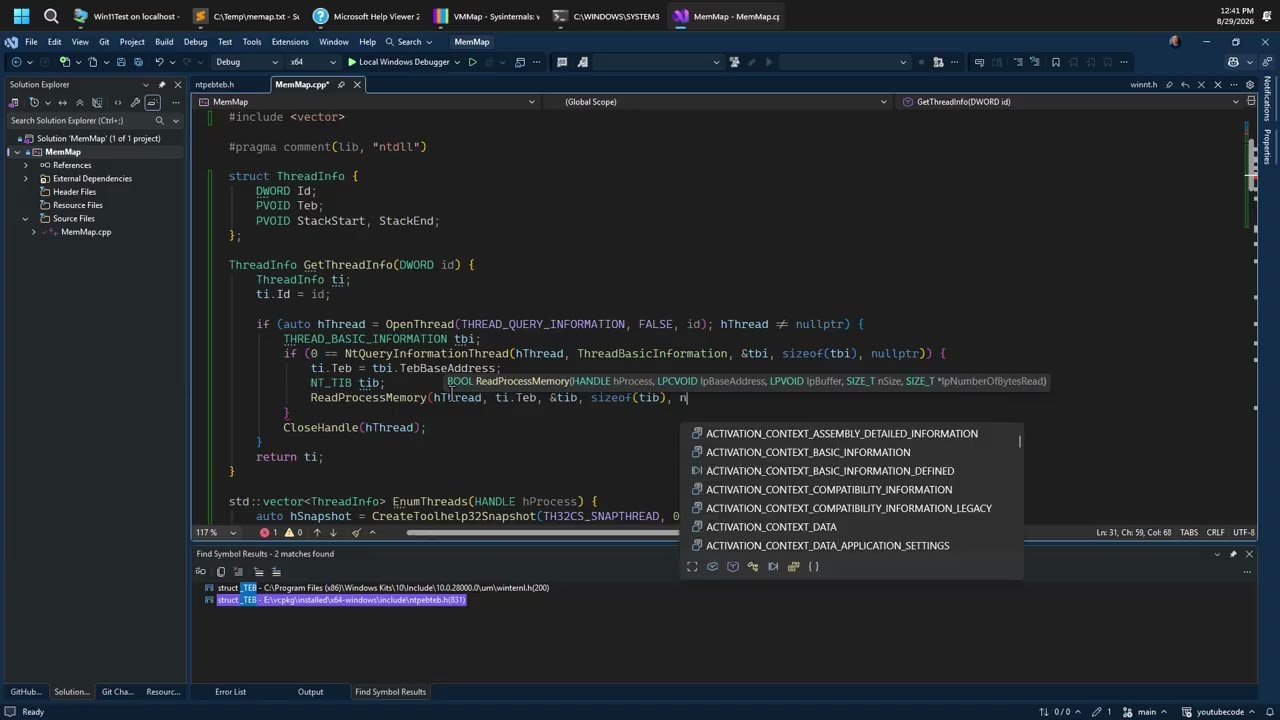
Pavel Yosifovich extends his MemMap tool to enumerate threads, locate each Thread Environment Block, and
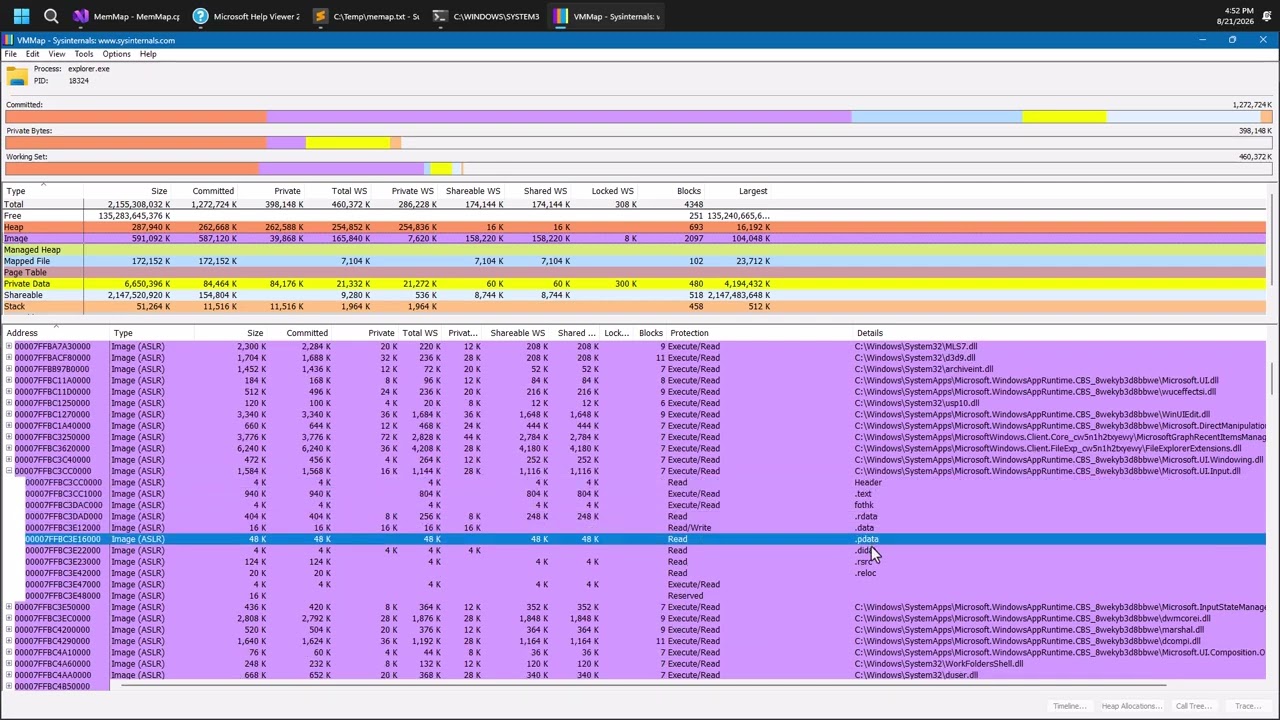
Pavel Yosifovich extends his MemMap tool with GetMappedFileName, then converts raw NT device paths into
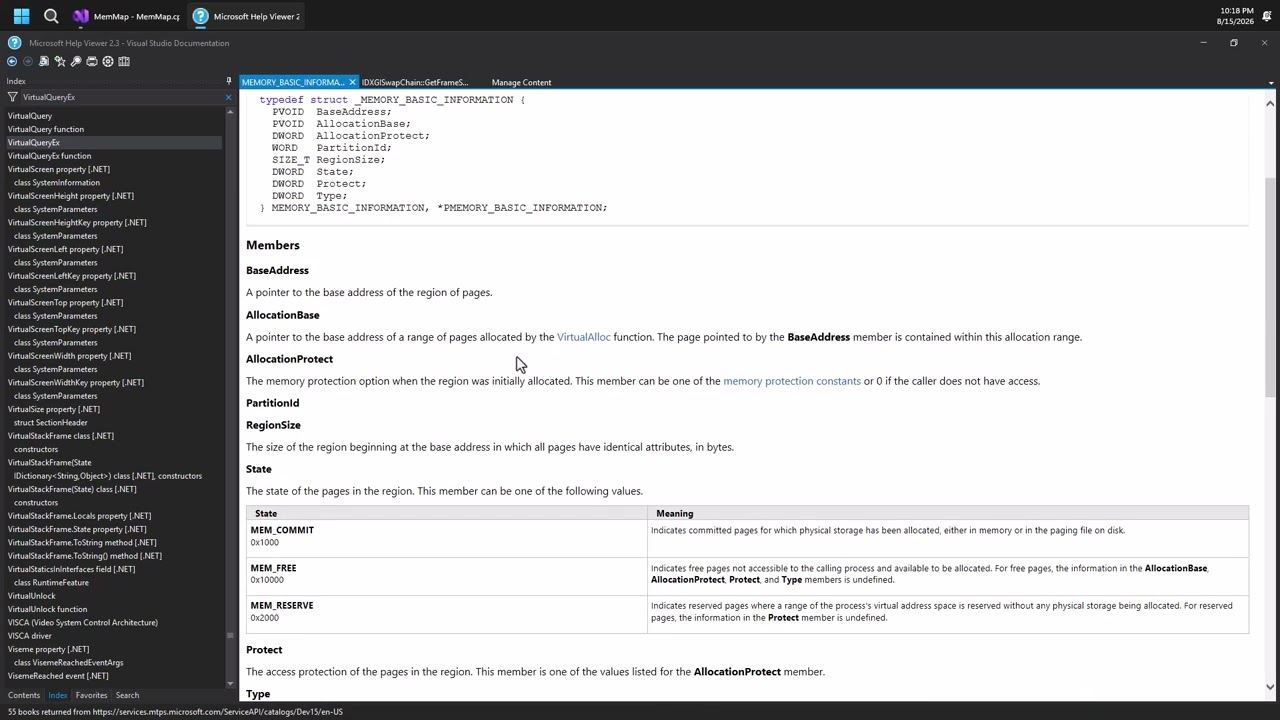
Pavel Yosifovich writes a C++ tool that reads a Windows process’s memory map with VirtualQueryEx,
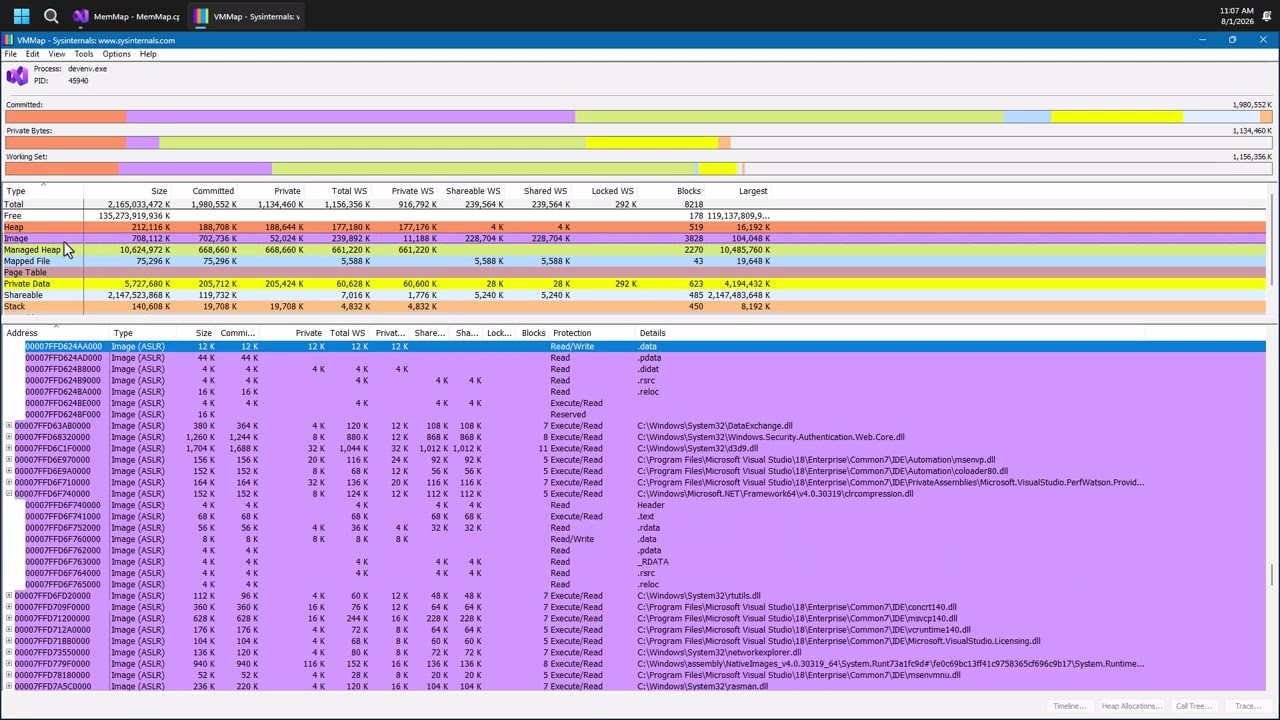
Pavel Yosifovich uses VMMap to break down a process’s memory layout, for developers and researchers
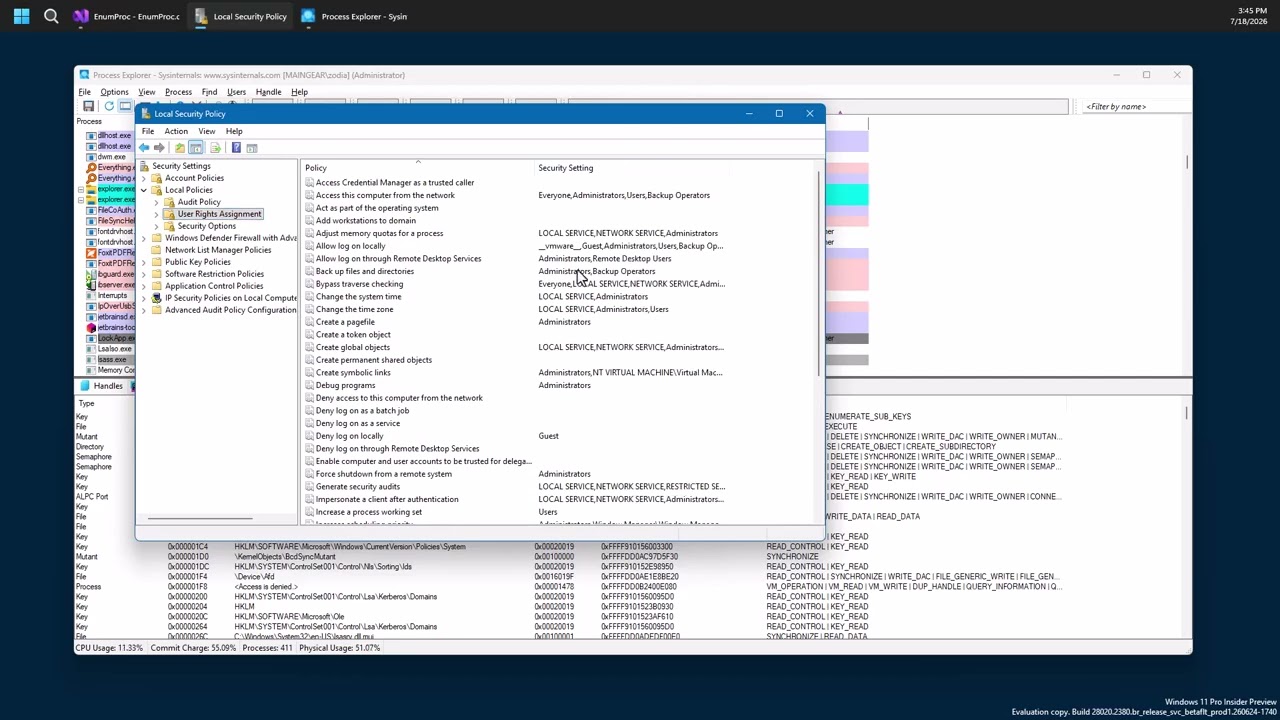
Pavel Yosifovich explains what Windows privileges are, why they live in the token, and how