Complete your Windows API foundation with DLLs, security and COM. In the final part of the series, Pavel Yosifovich, author of Windows 10 System Programming and co-author of Windows Internals, covers building and loading DLLs, DllMain and the loader lock, DLL injection techniques, access tokens, privileges, UAC and security descriptors, COM as a client, and the Win32 windowing model.
or $100 X 2 installments



9+ hours
on-demand video
Demos
live-coded in Visual Studio
43
video lessons
3
downloadable resources
9 CPE
CEU credits, self-reported
Certification
Certificate of completion
Three Windows topics trip up even experienced developers. DLLs look simple until a DllMain deadlocks under the loader lock. The security model looks like a permissions checkbox until a process runs with the wrong token, a privilege is not enabled or UAC virtualizes a write. COM looks like a single CoCreateInstance call until it fails with “class not registered”. This final part of the series explains all three from the API up.
In this course Pavel Yosifovich completes the Windows System Programming series. You build DLLs and export functions, variables and classes, compare implicit, explicit and delay-load linking, write a safe DllMain and use thread local storage. You then see how DLL injection is built from documented APIs (remote threads, APCs and Windows hooks), as a study of the API rather than an attack course. The security module covers the logon architecture, SIDs, access tokens, launching processes as another user and impersonation, privileges, security descriptors and access checks, UAC and integrity levels. The COM module is a client-side introduction to activation, smart pointers, type libraries and registration, and the course ends with the Win32 windowing model.
The course is a recording of a live class: 43 video lessons, with the slides, a labs PDF and the code. The topics are live-coded in Visual Studio and inspected with Process Explorer and other tools. Every video has English captions, and you learn at your own pace with lifetime access.
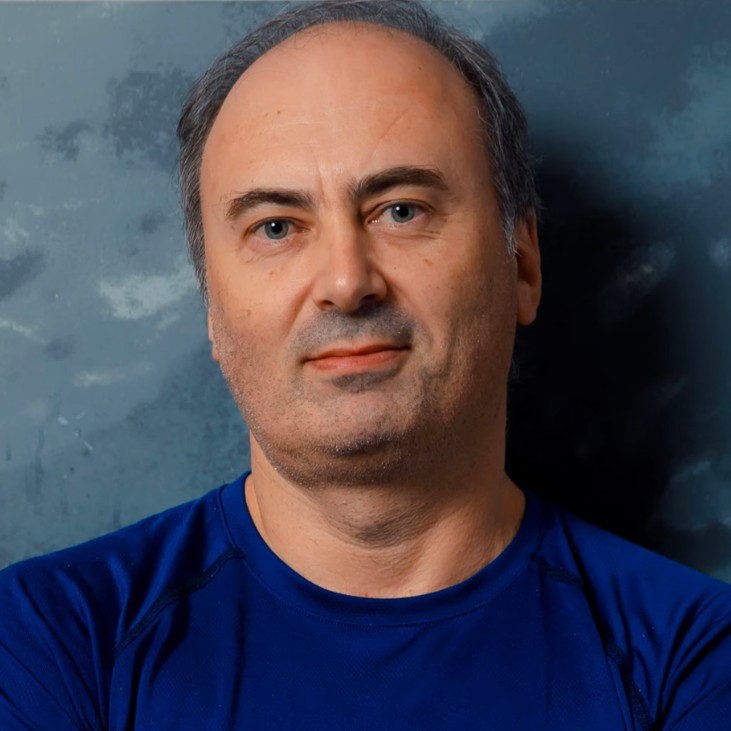
Pavel is the author of “Windows 10 System Programming”, “Windows Kernel Programming” and “Windows Native API Programming”, the co-author of “Windows Internals, 7th Edition, Part 1” (Microsoft Press), and a Microsoft MVP, with more than 25 years as a developer, consultant, trainer, author and speaker.
He writes Windows system software every day, and teaches the API the same way: with the internals behind each call, the tools to see what is happening, and labs that turn every topic into a working program.
Not the right fit if you have not yet covered handles, threads, synchronization and memory (take part 1 and part 2 first), if you want to write COM servers in depth (take COM Programming 1), or if you are looking for offensive tradecraft.
Windows System Programming 3 is the final part of the three-part series on the documented Windows API. Windows System Programming 1 covers the API conventions, kernel objects and processes, and Windows System Programming 2 covers jobs, threads, synchronization, I/O and memory. This part completes the foundation with DLLs, security, COM fundamentals and windowing.
Every topic is live-coded in Visual Studio and inspected with tools such as Process Explorer, OleView and Spy++, so you see exactly what the code does to the system.
Almost every “access denied”, every elevation prompt and every surprise from UAC comes down to tokens, privileges, integrity levels and security descriptors. Developers of services, installers, administration tools and security products need to understand them to write software that works correctly with least privilege. Security researchers need the same knowledge to understand what a process can and cannot do, and how DLLs end up loaded where they should not be.
DLLs are how nearly all Windows code is packaged and loaded, COM is how much of Windows exposes its functionality, and windows and message loops are how every desktop application works. Together with parts 1 and 2, this course gives you the complete user-mode foundation for COM Programming 1, GUI Programming with WTL and Windows Kernel Programming 1. It is part of the Windows Master Developer learning path and the Windows System Programming Bundle.
An overview of the final part of the series and its four topics: dynamic link libraries, Windows security, an introduction to COM, and basic windowing. The slides, the labs PDF and the code are available here.
DLLs from end to end. You learn their structure and purpose, build a DLL in Visual Studio and export functions, variables and classes with declspec or a module definition file, and consume it with implicit and explicit linking, including name mangling. The chapter covers DllMain and its reason codes, the loader lock, and thread local storage. It also shows how DLL injection is built from documented APIs, with a remote thread, a user-mode APC and Windows hooks, and how visible each method is.
The Windows security model in code. The chapter covers the logon architecture and how access tokens are created, security identifiers and their lookup APIs, primary and impersonation tokens, logon sessions and the UAC split token. You learn to query token information, launch processes under another identity or elevated, impersonate, and enable privileges. Then security descriptors, ACEs and SDDL, how the access check is decided, User Account Control and virtualization, running elevated, and integrity levels.
A client-side introduction to COM. You learn why COM exists, interfaces and IUnknown, GUIDs and HRESULTs, and in-process and out-of-process servers. You follow a BITS background download client, rewrite it with ATL and WIL smart pointers, and trace what CoCreateInstance does underneath: class factories and registry keys. The chapter also covers OleView, type libraries and #import, registration with 32-bit and 64-bit views, and Explorer extensibility such as icon handlers.
The Win32 windowing model and a course wrap-up. You build a basic GUI application to understand window classes, window creation, the message loop, window procedures and painting, see why blocking the UI thread makes a window stop responding, and keep it responsive with the thread pool and custom messages. The chapter demonstrates WinSpy and Spy++ and ends with a recap and further resources.
Yes, or equivalent knowledge. This is the final part of the series, and lessons such as DLL injection reuse the process, thread and memory APIs from Windows System Programming 1 and Windows System Programming 2.
No. DLL injection is shown as a combination of documented Windows APIs, with notes on how visible each method is, as part of understanding DLLs and processes. For the security track, see Malware Analysis and Development.
It covers the logon architecture, SIDs, access tokens, launching processes as another user, impersonation, privileges, security descriptors and access checks, UAC, virtualization and integrity levels, all in code.
No. The COM module is a client-side introduction: activation, smart pointers, type libraries and registration. Writing COM servers, ATL and apartments are covered in COM Programming 1 and COM Programming 2.
Only the fundamentals: window classes, the message loop, window procedures and painting, and keeping the UI responsive. For building real GUI applications in C++, take GUI Programming with WTL.
A Windows 10 or 11 PC with Visual Studio and its C++ workload, plus free tools such as Process Explorer, OleView and Spy++. Some demos need administrator rights.
The topics are live-coded in Visual Studio during the lessons, and a labs PDF with the lab code is included as a download.
Recorded and self-paced. It is a recording of a live class. You get lifetime access, and every video has English captions.
COM Programming 1 if COM is relevant to your work, GUI Programming with WTL for desktop applications, or Windows Kernel Programming 1 to move into kernel mode. All are part of the Windows Master Developer learning path.
Yes. When you complete every lesson you receive a certificate of completion and a Credly digital badge. The course also earns 9 CPE/CEU credits, which you self-report to your certification body using your certificate.
Yes. The DLL Introduction lesson is free to preview. Watch it on the course page.
43 video lessons, more than 9 hours of video, plus lab time. Most students spread it over a couple of weeks.
$199 as a single payment, or 2 monthly payments of $100 ($200 in total). All three parts together are cheaper as the Windows System Programming Bundle: $749, or 5 payments of $150.
Lifetime access to the purchased course.
Yes. Refunds are available up to 14 days after purchase, to the original payment method. Email [email protected].
Pavel is the author of “Windows 10 System Programming”, “Windows Kernel Programming” and “Windows Native API Programming”, the co-author of “Windows Internals, 7th Edition, Part 1” (Microsoft Press), and a Microsoft MVP, with more than 25 years as a developer, consultant, trainer, author and speaker.
He writes Windows system software every day, and teaches the API the same way: with the internals behind each call, the tools to see what is happening, and labs that turn every topic into a working program.
Complete your Windows API foundation with DLLs, security and COM. In the final part of the series, Pavel Yosifovich, author of Windows 10 System Programming and co-author of Windows Internals, covers building and loading DLLs, DllMain and the loader lock, DLL injection techniques, access tokens, privileges, UAC and security descriptors, COM as a client, and the Win32 windowing model.
